
Smart contracts are powerful, but they operate under strict computational limitations.
They cannot efficiently process large historical datasets, perform complex analytics, or access arbitrary blockchain data without increasing execution costs.
This limitation becomes increasingly important as decentralized applications become more sophisticated.
ZK Coprocessors introduce a new approach.
They allow complex computations to be performed outside the blockchain while generating cryptographic proofs that enable smart contracts to verify the results.
This creates a powerful combination:
Off-chain computation + verifiable results + on-chain execution
What Is a ZK Coprocessor?
A ZK Coprocessor is an external computation layer that performs complex operations outside the blockchain and generates a Zero-Knowledge Proof demonstrating that the computation was executed correctly.
Instead of forcing a smart contract to perform every calculation itself, the expensive computation can happen externally.
The blockchain only needs to verify the resulting proof.
This effectively gives smart contracts access to additional computational capabilities without requiring them to execute the entire workload on-chain.
Why It Matters
1️⃣ More Powerful Smart Contracts
Applications can perform computations that would be impractical or too expensive to execute directly on-chain.
2️⃣ Lower Computational Costs
Large calculations can happen off-chain while only a compact proof is verified on-chain.
3️⃣ Historical Data Access
Applications can analyze blockchain history and use the results without storing and processing all historical information inside the smart contract.
4️⃣ Verifiable Off-Chain Computation
The blockchain does not need to blindly trust an external computation provider because the result can be cryptographically verified.
How It Works
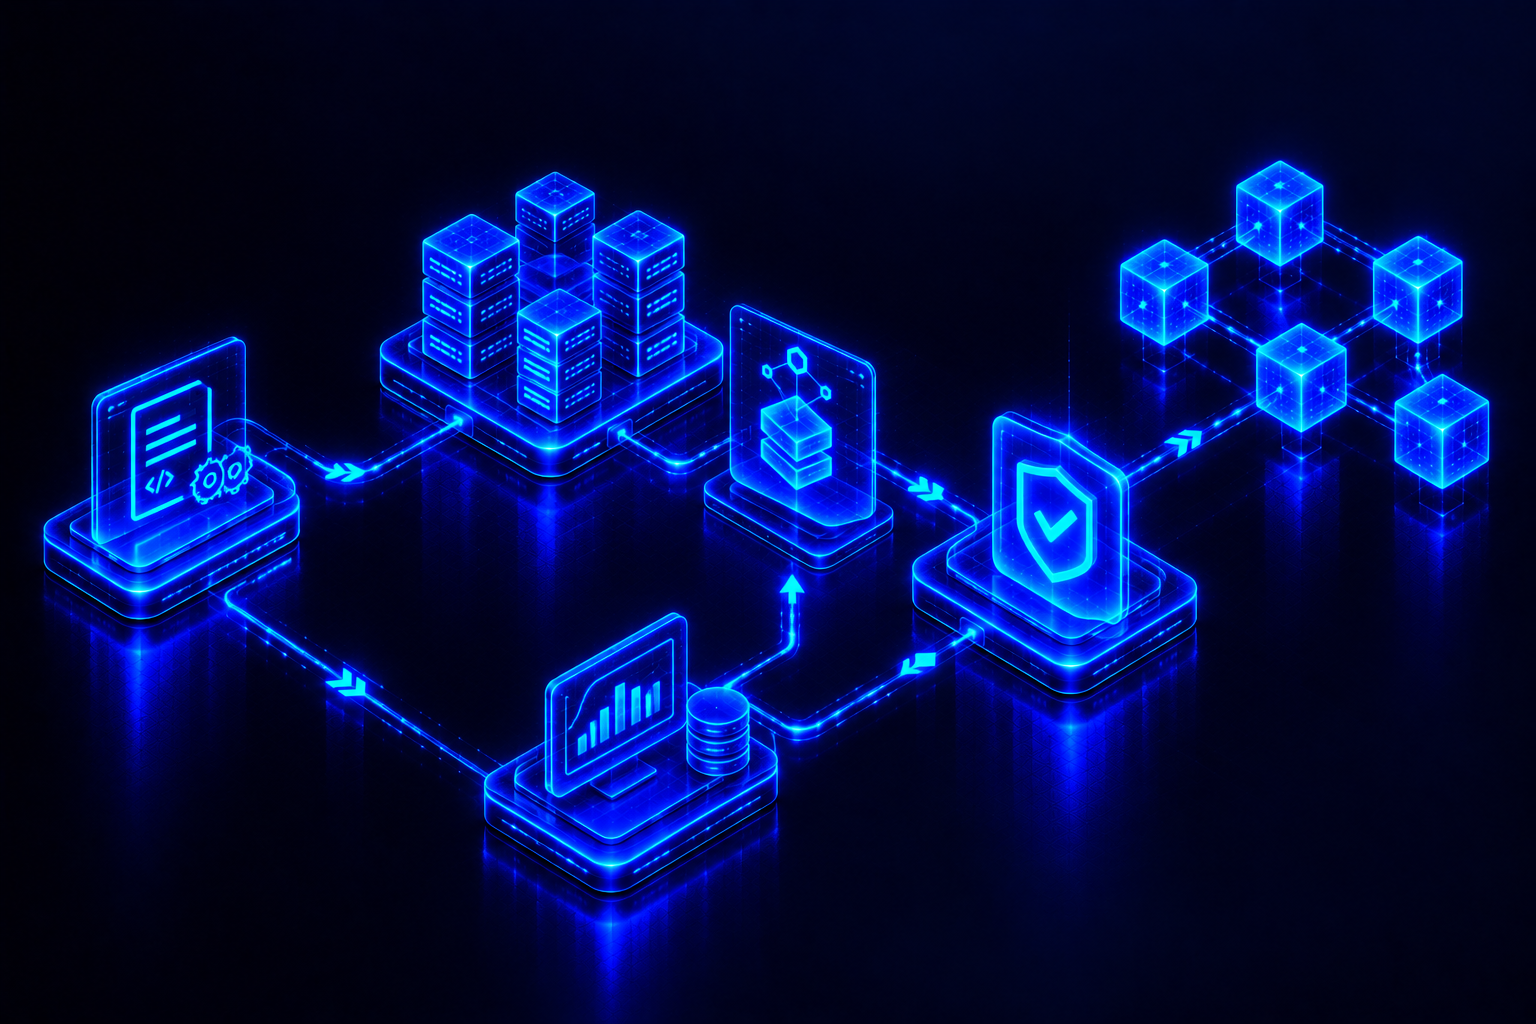
A typical ZK Coprocessor architecture includes several components:
🔹 Smart Contract
Defines the computation or result that the application needs.
🔹 Off-Chain Computation
An external system processes potentially large amounts of data or performs complex calculations.
🔹 Zero-Knowledge Proof
The computation provider generates a cryptographic proof showing that the result satisfies the required conditions.
🔹 On-Chain Verifier
The smart contract verifies the proof and uses the resulting information.
This architecture allows expensive computation to remain off-chain while maintaining verifiability on-chain.
Use Cases
DeFi Analytics
Smart contracts could use historical market data to support more sophisticated financial strategies.
On-Chain Reputation
Applications could calculate user activity or historical behavior without storing every detail directly on-chain.
Gaming
Complex player statistics and historical game data could be processed externally and verified before affecting on-chain game logic.
DAO Governance
Governance systems could use historical participation, reputation, or contribution data when determining eligibility or voting power.
ZK Coprocessors vs. Traditional Oracles
Traditional blockchain oracles primarily provide external information to smart contracts.
ZK Coprocessors introduce a different capability.
Instead of simply saying:
“Here is the data.”
The system can provide:
“Here is the result, together with cryptographic evidence that it was calculated correctly.”
This distinction can become particularly valuable when applications need complex computations rather than simple data feeds.
Challenges
ZK Coprocessors are still an emerging technology and face several challenges:
- Proof-generation costs
- Computational complexity
- Development complexity
- Verification design
- Data availability
- Infrastructure scalability
As workloads become larger, generating proofs efficiently becomes increasingly important.
The technology therefore depends not only on cryptographic innovation but also on advances in specialized hardware and proof-generation systems.
The Future of Smart Contracts
Smart contracts were originally designed to execute predefined logic on-chain.
ZK Coprocessors could expand this model by giving decentralized applications access to much larger computational resources without sacrificing verifiability.
Instead of choosing between powerful off-chain computation and trustless on-chain verification, developers can increasingly combine the two.
This could enable a new generation of applications built around historical data, complex analytics, personalized logic, and sophisticated financial strategies.
The future is computational:
smart contracts may not need to perform every calculation themselves—they only need to be able to verify that the calculation was done correctly.
Leave a Reply