
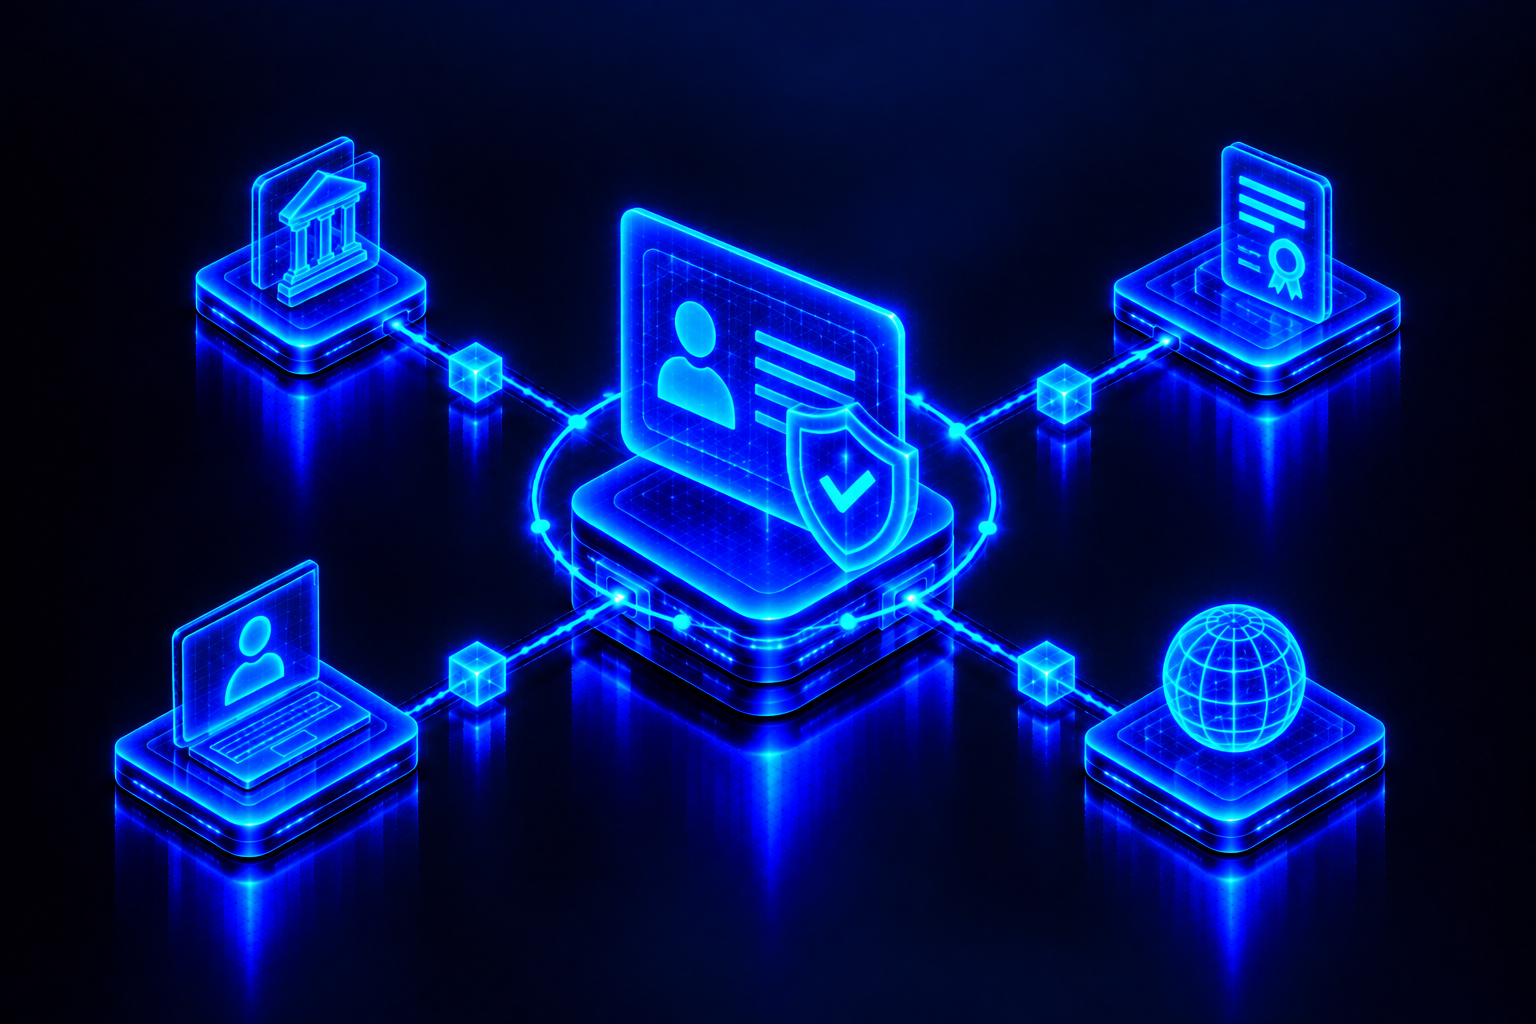
The digital world depends on identity.
From accessing financial services to signing into applications and verifying personal information, users constantly need to prove who they are or demonstrate that they meet specific requirements.
However, traditional digital identity systems often rely on centralized organizations that store and manage personal information.
This creates challenges around privacy, data security, interoperability, and user control.
Decentralized Identity (DID) introduces a different approach.
Instead of depending entirely on centralized identity providers, decentralized identity systems allow individuals and organizations to manage digital identifiers and present verifiable credentials across different services.
By combining cryptography, digital credentials, and blockchain-compatible infrastructure, decentralized identity can help build a more user-controlled identity ecosystem.
What Is Decentralized Identity?
Decentralized Identity is an approach to digital identity that reduces dependence on a single organization to create, manage, and verify identities.
A central concept is the Decentralized Identifier (DID): an identifier designed to be created and controlled independently of a centralized identity provider.
Depending on the method used, a DID can resolve to information describing how to interact with its controller or verify associated cryptographic keys.
Decentralized identity systems can also use verifiable credentials—digitally signed statements issued by trusted organizations.
For example, a university could issue a digital credential confirming that someone holds a degree. The individual could then present that credential to another organization for verification.
The goal is to make identity more portable, verifiable, and controllable by the people and organizations it represents.
Why It Matters
1. Greater User Control
Individuals can manage their identifiers and credentials without relying on a single platform to maintain their entire digital identity.
2. Improved Privacy
Systems can be designed to disclose only the information required for a particular interaction.
For example, a service may need confirmation that a user is over a certain age rather than their full date of birth.
3. Cross-Platform Verification
Verifiable credentials can be presented to different services without requiring every organization to maintain a separate identity database.
4. Reduced Identity Fragmentation
Portable identity credentials can help users avoid repeatedly completing the same verification process across unrelated platforms, where the receiving services accept compatible credentials.
How It Works
A decentralized identity ecosystem typically includes several components.
🔹 Decentralized Identifier
An identifier associated with a controller and supported by a DID method.
🔹 Issuer
An organization or entity that creates and digitally signs a credential, such as a professional certification or proof of membership.
🔹 Holder
The individual or organization that controls a credential and decides when to present it, subject to the system’s design.
🔹 Verifier
A service that checks whether a presented credential is authentic, valid, and appropriate for the requested purpose.
🔹 Verification Infrastructure
Cryptographic keys, trust frameworks, revocation mechanisms, and sometimes blockchain-based registries help participants verify relevant information.
A typical interaction follows this process:
Issue → Hold → Present → Verify
The credential can be verified without requiring the issuer to participate in every individual verification request.
Decentralized Identity vs. Traditional Identity Systems
Traditional identity systems commonly depend on centralized providers.
A website may store user information in its own database or rely on a third-party provider to authenticate users.
This model can be convenient, but it may create isolated identity silos and concentrate sensitive information.
Decentralized identity introduces a more portable model in which identifiers and credentials can be controlled and presented across compatible systems.
However, decentralization does not mean that every organization disappears from the process.
Trusted institutions may still issue credentials, and verifiers must still decide which issuers and credentials they accept.
The key difference is that identity verification can become more portable without requiring every verifier to control the underlying identity.
The Role of Blockchain
Blockchain can support decentralized identity by providing infrastructure for recording and verifying selected information.
For example, a blockchain network may be used to publish public keys, register issuer information, or maintain references to credential-related data.
However, storing complete identity records directly on a public blockchain is generally undesirable because personal information can be difficult or impossible to remove once published.
A privacy-conscious architecture keeps sensitive credentials and personal data off-chain whenever possible, using cryptographic verification and carefully designed references instead.
Blockchain is therefore one possible component of decentralized identity—not a requirement for every DID method or credential system.
Use Cases
Digital Credentials
Universities, training providers, and professional organizations can issue credentials that recipients present to employers or other institutions.
Financial Services
Financial institutions can verify selected customer attributes or compliance credentials while reducing unnecessary sharing of personal information.
Healthcare
Patients could use digital credentials to demonstrate authorization or share specific information with healthcare providers, subject to applicable privacy and regulatory requirements.
Enterprise Access
Organizations can use verifiable credentials to support employee access, professional certifications, and partner verification across systems.
Web3 Applications
Decentralized applications can use identity credentials to establish eligibility, membership, reputation, or access rights without making every interaction dependent on a centralized account provider.
Selective Disclosure and Privacy
One of the most important capabilities in privacy-focused identity systems is selective disclosure.
Traditional verification often requires users to share more information than the receiving service actually needs.
For example, proving eligibility for a service might require only confirmation of a particular attribute.
A credential system with selective disclosure can allow the holder to reveal only the relevant information, depending on the credential format and verification mechanism.
Some systems can also use Zero-Knowledge Proofs to demonstrate that a condition is satisfied without revealing the underlying value.
These capabilities can reduce unnecessary data exposure, although they do not automatically prevent every form of tracking or correlation.
Privacy still depends on how identifiers, metadata, credentials, and verification requests are designed.
Challenges
Despite its potential, decentralized identity faces several important challenges:
- Credential interoperability
- Key recovery and account security
- Issuer trust and governance
- Credential expiration and revocation
- Privacy and correlation risks
- Regulatory compliance
- Usability for non-technical users
A decentralized identifier alone does not prove that a real-world claim is true.
For example, a credential may be cryptographically authentic but still contain inaccurate information if the issuer made a mistake or acted dishonestly.
Reliable systems therefore need trustworthy issuers, clear verification policies, secure key management, and effective recovery mechanisms.
The Future of Digital Identity
As digital services become increasingly interconnected, people need ways to prove relevant information without repeatedly surrendering control of their personal data.
Decentralized identity offers a framework for making credentials more portable and verification more flexible.
Instead of maintaining a separate identity profile for every service, users could present trusted credentials wherever compatible systems accept them.
This could support a digital ecosystem in which identity is less dependent on individual platforms and more focused on verifiable claims, user choice, and privacy-conscious design.
Conclusion
Decentralized Identity represents an important shift in how digital identity can be managed and verified.
By combining decentralized identifiers, verifiable credentials, cryptography, and compatible verification infrastructure, these systems can reduce dependence on centralized identity silos while giving users more control over what they share.
The technology still faces challenges involving interoperability, trust, privacy, and recovery, but its potential extends across finance, healthcare, enterprise systems, and Web3 applications.
As digital interactions continue to expand, identity infrastructure will play an increasingly important role in determining who can access services and how personal information is protected.
The future of digital identity is not simply about proving who you are. It is about proving what matters while sharing only what is necessary.
Leave a Reply